tools
Pulumi IaC
Pulumi IaC lets teams define, deploy, test, and manage cloud infrastructure using general-purpose programming languages.
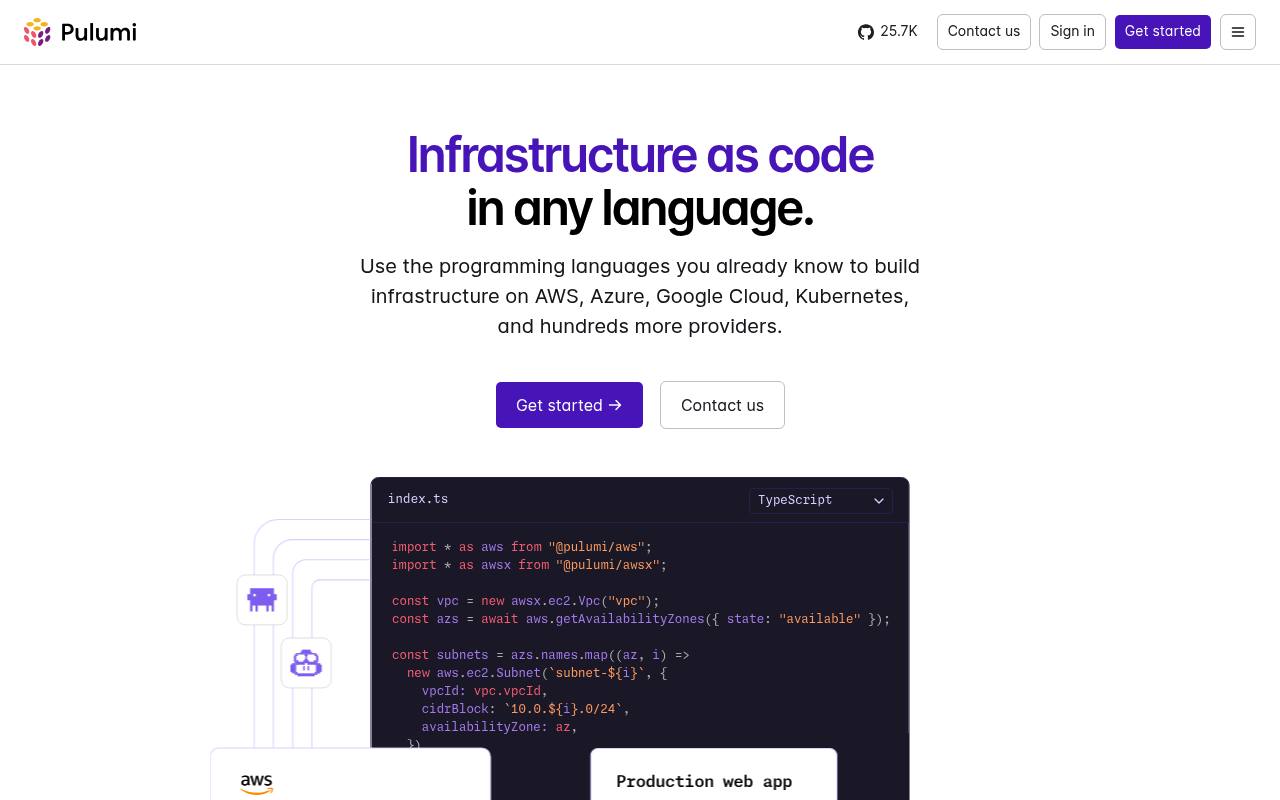
Pulumi IaC provisions infrastructure across AWS, Azure, Google Cloud, Kubernetes, and other providers. Engineers can use TypeScript, JavaScript, Python, Go, .NET, Java, HCL, or YAML, then manage changes through Git and CI/CD.
It includes reusable components, previews, testing, encrypted state, secrets management, policy as code, and Automation API. The open-source engine is free; Pulumi Cloud plans add collaboration, governance, and usage-based charges for managed resources and related services.
Features
- Define infrastructure with TypeScript, JavaScript, Python, Go, .NET, Java, HCL, or YAML
- Deploy to AWS, Azure, Google Cloud, Kubernetes, and hundreds of providers
- Preview infrastructure changes before deployment
- Run unit tests and integration tests against ephemeral environments
- Create reusable infrastructure components and publish them to package registries
- Manage encrypted state, secrets, version history, and audit trails
- Enforce security and compliance with policy as code
- Use Automation API to embed infrastructure operations in applications
Use cases
- Provision cloud infrastructure from version-controlled programs
- Review infrastructure changes in pull requests
- Test infrastructure in ephemeral pre-production environments
- Build reusable infrastructure components for engineering teams
- Automate deployments through GitHub Actions, GitLab, Jenkins, or other CI/CD systems
- Create internal platforms and custom infrastructure tools with Automation API
Pros
Cons
Latest updates
- Manage Pulumi ESC change requests from the CLI
The pulumi env change-request command lets users work with ESC change requests from the CLI.
- AI infrastructure on tap with the Pulumi AICR provider
Pulumi introduced the AICR provider for managing AI infrastructure.
- Assign policy groups by stack and account tags
Policy groups now support tag matching conditions for stacks and cloud accounts.
- Pulumi ESC now issues OIDC tokens for any service
Pulumi ESC can now issue short-lived OIDC tokens for any service that accepts them using fn::open::oidc.
- Scale your team's use of AWS IAM account access manager with Pulumi
Pulumi AWS and AWS Native providers now include accountaccess resources for managing AWS IAM account access manager.
Capabilities
- Inline completion — “Get autocomplete, type checking, and all your favorite IDE features.” source
- Reviews pull requests — “Neo code reviews” source
- Command line — “Neo in the CLI” source
- Self-hosted — “or self-host if required.” source
- API — “Embed Pulumi in your app.” source
- Official SDKs — “Multi-language SDKs” source
Get it
Security
Pricing
- Starting price
- $40/mo
- Prices checked
- 2026-11-05
Free
Free
- 1 user
- IaC state management
- Pulumi Deployments
- Basic Pulumi ESC
- Unlimited projects, stacks, and environments
- Up to 500 workflow minutes
Essentials
- $40 /month
- Unlimited users
- Secure collaboration and CI/CD
- Neo code reviews and Slack integration
- Resource Search and Property Search
- OIDC and org access tokens
- Automatic secrets rotation
Pro
- $400 /month
- SAML/SSO and advanced RBAC
- Organization-managed policy enforcement
- Preventative policies
- Custom policy packs
- Neo scheduled tasks
- Drift detection and remediation
Enterprise
Price on request
- Self-hosting available
- Conformance packs for CIS, CIS Kubernetes, CMMC, HITRUST, ISO 27001, NIST, and PCI DSS
- Automatic group & user sync (SCIM)
- Automated audit log export
- Unlimited custom policy packs
- Policy remediation