tools
Dropzone AI SOC Analyst Platform
Dropzone AI investigates security alerts, gathers evidence across connected tools, and gives SOC teams auditable findings and response actions.
In inglese
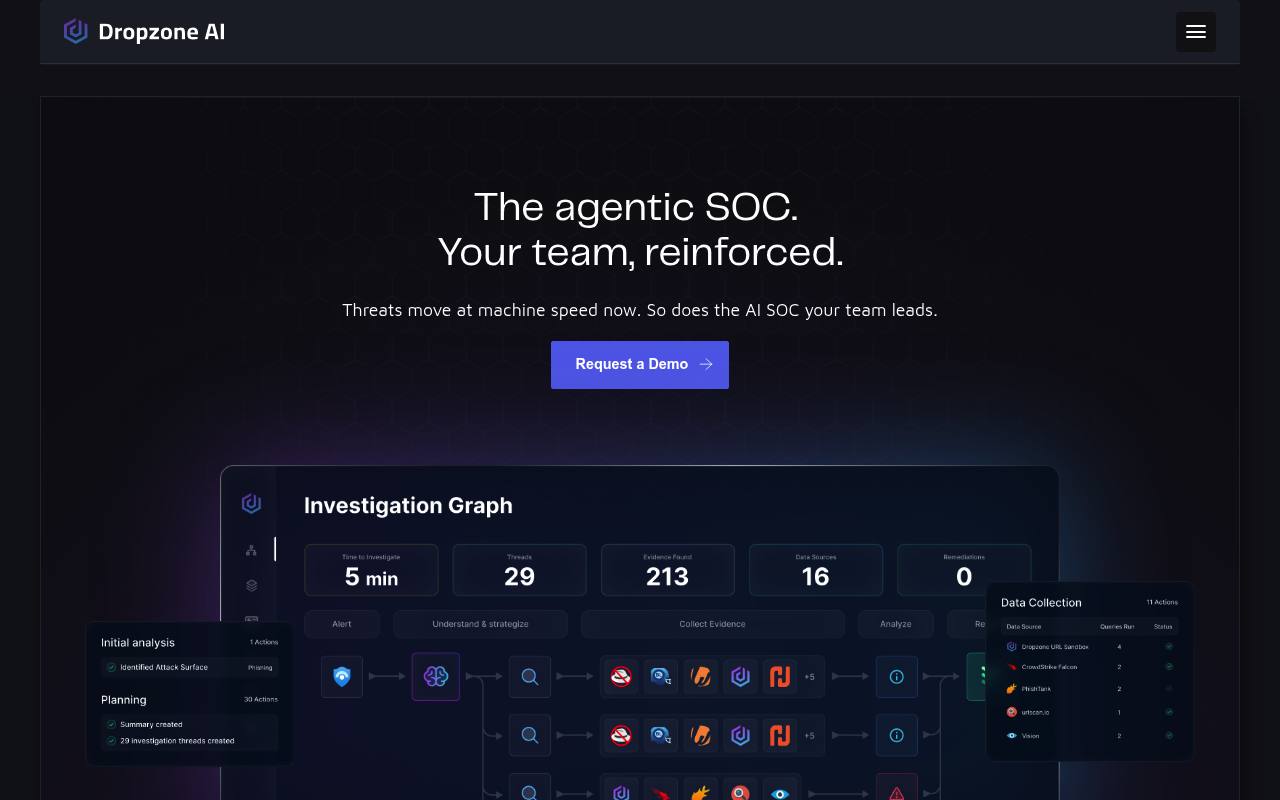
Dropzone AI is a web-based SOC platform for security teams and MSSPs. Its AI SOC Analyst investigates alerts across SIEM, EDR, cloud, identity, email, and other connected tools, then produces findings, evidence, and conclusions for analyst review.
The platform includes natural-language chat, context memory, custom investigation strategies, and automated containment actions such as blocking malicious IPs or disabling compromised accounts. Pricing is based on investigation capacity and is not publicly listed; enterprise and MSSP deployments have custom pricing.
Features
- Investigates security alerts end to end across connected security tools
- Collects evidence from SIEM, EDR, cloud, identity, email, and other systems
- Produces findings, evidence, reasoning, and remediation details
- Provides natural-language chat for tactical lookups and ad-hoc investigations
- Uses context memory to retain environment-specific knowledge and feedback
- Supports custom investigation strategies, authorization rules, and business context
- Triggers containment actions such as blocking IPs and disabling accounts
- Offers 90+ integrations through existing security-tool APIs
Use cases
- Triage large alert queues and separate likely threats from false positives
- Review evidence-backed investigations during human SOC approval workflows
- Query connected security data with natural-language chat
- Investigate incidents across SIEM, endpoint, identity, cloud, and email systems
- Automate containment after an AI-confirmed threat
- Scale alert investigation for enterprise SOCs and MSSPs
Pros
Cons
Capabilities
- Automations — “AI Threat Hunter runs on a schedule, or on demand, as a steady part of how the SOC operates.” source
- AI agents — “You set the strategy. The AI SOC agents deliver it at a scale and consistency beyond human capacity.” source
- Connects your apps — “90+ integrations across SIEM, EDR, cloud, identity, and email.” source
- Admin controls — “Anyone you provision in your organization can access full reports, use our chatbot and fine-tune the AI Analyst behavior.” source
Get it
Pricing
- Starting price
- $36000/yr
- Prices checked
- 2026-09-25
AI SOC Analyst
- 36000 USD
- Up to 4,000 full investigations per year per AI analyst
- Unlimited users
- All available security alert categories
- All pre-built integrations
- AI chatbot for ad-hoc investigation
- 8-hour customer support SLA
Enterprise Plan
Price on request
- Dedicated single-tenant environment
- Custom workflow
- Premium support and SLAs
MSSP
Price on request
- Dedicated multi-tenant environment
- Pool your AI analysts across your customer base
- Custom implementation service
- Premium support and SLAs